

EN 18235-2:2026
(Main)Trusted data transactions - Part 2: Trustworthiness requirements
- Abstract
This document provides trustworthiness requirements and guidance for data space participants in support of trusted data transactions.
Specifically, it defines a set of foundational principles for trusted data transactions, and establishes general requirements and guidance that apply to all phases of a trusted data transaction, and specific requirements for each phase of a trusted data transaction.
This document applies to all types of organizations participating in data spaces, regardless of their type or size.
- Status
- Published
- Publication Date
- 10-Nov-2026
- Technical Committee
- JTC 25 - Data management, Dataspaces, Cloud and Edge
- Drafting Committee
- WG 2 - Dataspaces
- Current Stage
- 6060 - Definitive text made available (DAV) - Publishing
- Start Date
- 11-Nov-2026
- Due Date
- 31-Oct-2026
- Completion Date
- 11-Nov-2026
EN 18235-2:2026, published by CEN, sets trustworthiness requirements and guidance for data space participants involved in trusted data transactions. It defines foundational principles and phase-by-phase requirements for grant rights, publication, discovery, negotiation, data sharing, and data access and usage, and it applies to organizations of any type or size participating in data spaces.
What does EN 18235-2:2026 specify?
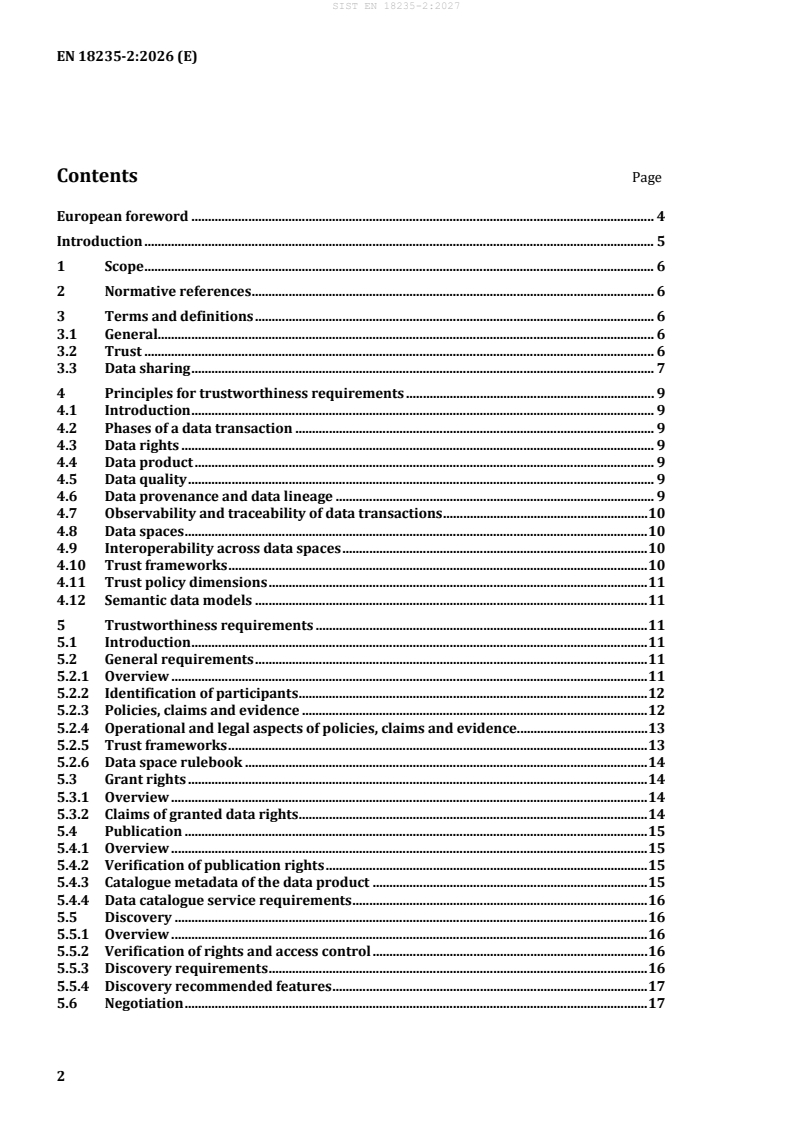
EN 18235-2:2026 specifies the trustworthiness basis for trusted data transactions in data spaces. It is organized into general principles in Clause 4, detailed requirements in Clause 5, definitions in Clause 3, and two informative annexes.
| Annex | What it covers |
|---|---|
| A | Trust frameworks: purpose, mechanisms, elements, and use in data spaces |
| ZA | Relationship with Regulation (EU) 2023/2854 and the interoperability requirements it aims to cover |
The document starts with the scope, then defines the terms used throughout, then sets out the principles that underpin trusted data transactions. Clause 5 follows the lifecycle of a transaction, so a reader can map the standard to real operating steps rather than treat trust as a single check.
What are the key requirements of EN 18235-2:2026?
EN 18235-2:2026 requires trusted data transactions to be handled through verifiable identity, machine-readable claims, documented trust frameworks, and controls that follow the transaction from onboarding to data use. In practice, this means participants, platforms, and governance bodies each need clear evidence, records, and access controls.
Participant identity and trust evidence
Clause 5.2.2 requires identity evidence to be machine-readable, linked to the identity provider, and tied to a unique participant identifier within that provider’s domain. That matters because automated trust checks only work if a system can reliably match a participant to a known identity source.
Clauses 5.2.3 and 5.2.4 require policies, claims, and evidence to be identifiable, integrity-protected, validatable, and presentable in structured form. The practical effect is that a participant should be able to prove who issued a statement, what it applies to, and whether it is still valid before anyone relies on it.
Trust frameworks and data space governance
Clause 5.2.5 requires a trust framework to define identification methods, a taxonomy for policies, claims and evidence, semantic models, criteria for trust anchors and trust services, and a trusted list of those anchors and services. This gives a data space a common basis for automated checks and helps different parties interpret trust information the same way.
Clause 5.2.6 requires the data space rulebook to set validation criteria for onboarding claims, a mechanism to verify membership, a mechanism to validate rulebook claims, and a mechanism to validate claims from other data spaces where agreements exist. In practice, a data space governance authority must be able to confirm who belongs to the space and what claims it accepts.
Grant rights, publication and catalogue control
Clause 5.3 requires claims of granted data rights to include evidence of delegation, metadata describing the data products covered, the allowed kinds of users, relevant provenance and lineage, and any consent or permission conditions for personal or sensitive data. This is the part that shows whether the provider is actually allowed to publish, share, or license the data.
Clause 5.4 requires publication to be backed by verifiable publication rights, and it requires data catalogues to publish only authorized data products. Catalogue metadata must be current, machine-readable, include the required metadata, and state licence terms and restrictions, while catalogue operators must control who can publish or modify metadata. For operators, this means metadata governance is part of trust, not just a search function.
Discovery, negotiation, sharing and use
Clause 5.5 requires discovery services to control access to catalogues and data products and to present query results in a way that helps users judge relevance and suitability. They must also show access conditions, rights and licence terms, so a potential user can decide whether to proceed before entering a transaction.
Clause 5.6 requires the negotiated data usage contract to be recorded in a machine-readable way, with mandatory contractual elements, an unambiguous reference to the data product, the usage terms, and a commonly agreed standard. That makes the agreement usable as an operational and legal record instead of a loose email trail.
Clauses 5.7 and 5.8 require verification before sharing, before access, and before use. The provider must verify the user’s identity and authorizations, and the user must verify that usage permissions and consent are still valid before using the data. Both sides must also support agreed observability mechanisms, so transactions can be monitored and logged when the contract or regulations require it.
What terms does EN 18235-2:2026 define?
EN 18235-2:2026 defines the main trust and data-sharing terms used in the standard, so participants use the same language when checking rights, evidence, and transaction status.
- Claim - a statement that something is true, with any conditions or limits attached.
- Evidence - information that supports a claim.
- Policy - a set of rules for a particular purpose, such as who may use data or under what conditions.
- Reconciliation - the process of checking whether claims and evidence satisfy the relevant policy.
- Trustworthiness - a quality supported by verifiable evidence that can be used to establish trust.
- Trust framework - a set of requirements, rules, roles, responsibilities, and assessment mechanisms that support trust.
- Data space rulebook - the governance framework that sets the principles, processes, standards, protocols, rules, and practices for a data space.
- Observability - the ability to monitor and verify the state and behaviour of a trusted data transaction.
Who uses EN 18235-2:2026?
EN 18235-2:2026 is written for all types of organizations participating in data spaces, regardless of size. It is relevant to data rights holders, data providers, data users, data intermediaries, data space governance authorities, identity providers, catalogue operators, and discovery service operators.
In practice, it helps teams that design data space governance, operate data catalogues or discovery services, manage membership and onboarding, or assess whether a data transaction can proceed under agreed rights and conditions. It is also useful for legal, compliance, security, and quality teams that need traceable rules for data sharing.
Which standards are used with EN 18235-2:2026?
EN 18235-2:2026 has no normative references. It does, however, rely on prEN 18235-1 as the companion part that provides the terminology, concepts, and mechanisms for trusted data transactions.
| Referenced standard or document | What it contributes |
|---|---|
| prEN 18235-1 | Base terminology, concepts, and mechanisms for the series |
| ISO 8000 (all parts) | Example framework for data quality methodology in catalogue metadata |
| ISO/IEC 22123-1:2023 | Definition of interoperability |
| ISO/IEC 5259-1:2024 | Definition used for data provenance |
| ISO/IEC 5259-5:2025 | Definition used for principle |
| ISO/IEC TR 15443-1:2012 | Definition used for claim |
| ISO 19101-2:2018 | Definition used for policy |
| DSSC Data Spaces Blueprint v2.0 | Source for the data space rulebook concept |
What does the EN 18235-2:2026 document contain?
EN 18235-2:2026 contains a principles section, a requirements section, terms and definitions, and two informative annexes. Clause 4 explains the transaction phases and the concepts behind rights, data products, provenance, lineage, observability, interoperability, trust frameworks, and trust policy dimensions.
Clause 5 gives the operational requirements for identity, claims, evidence, membership, rights, publication, discovery, negotiation, sharing, access, usage, and observability. The document also includes detailed metadata requirements for catalogues and discovery services, plus a recorded contract requirement for negotiations.
Annex A explains how trust frameworks work in practice, including governance and process/technical dimensions, trust anchors, trust services, and trust lists. Annex ZA maps the standard to the interoperability requirements of Regulation (EU) 2023/2854 and identifies the clauses intended to support Article 33.
Get Certified
Connect with accredited certification bodies for this standard

BSI Group
BSI (British Standards Institution) is the business standards company that helps organizations make excellence a habit.

Bureau Veritas
Bureau Veritas is a world leader in laboratory testing, inspection and certification services.
DNV
DNV is an independent assurance and risk management provider.
Sponsored listings
Frequently Asked Questions
EN 18235-2:2026 is a standard published by the European Committee for Standardization (CEN). Its full title is "Trusted data transactions - Part 2: Trustworthiness requirements". This standard covers: This document provides trustworthiness requirements and guidance for data space participants in support of trusted data transactions. Specifically, it defines a set of foundational principles for trusted data transactions, and establishes general requirements and guidance that apply to all phases of a trusted data transaction, and specific requirements for each phase of a trusted data transaction. This document applies to all types of organizations participating in data spaces, regardless of their type or size.
This document provides trustworthiness requirements and guidance for data space participants in support of trusted data transactions. Specifically, it defines a set of foundational principles for trusted data transactions, and establishes general requirements and guidance that apply to all phases of a trusted data transaction, and specific requirements for each phase of a trusted data transaction. This document applies to all types of organizations participating in data spaces, regardless of their type or size.
EN 18235-2:2026 is classified under the following ICS (International Classification for Standards) categories: 35.030 - IT Security. The ICS classification helps identify the subject area and facilitates finding related standards.
EN 18235-2:2026 is associated with the following European legislation: EU Directives/Regulations: 2023/2854; Standardization Mandates: M/614. When a standard is cited in the Official Journal of the European Union, products manufactured in conformity with it benefit from a presumption of conformity with the essential requirements of the corresponding EU directive or regulation.
EN 18235-2:2026 is available in PDF format for immediate download after purchase. The document can be added to your cart and obtained through the secure checkout process. Digital delivery ensures instant access to the complete standard document.
Standards Content (Sample)
SLOVENSKI STANDARD
01-januar-2027
Zaupanja vredne podatkovne transakcije - 2. del: Zahteve za zanesljivost
Trusted data transactions - Part 2: Trustworthiness requirements
Vertrauenswürdige Datentransaktionen - Teil 2: Anforderungen an die
Vertrauenswürdigkeit
Transactions de données de confiance - Partie 2 : Exigences de crédibilité
Ta slovenski standard je istoveten z: EN 18235-2:2026
ICS:
35.030 Informacijska varnost IT Security
2003-01.Slovenski inštitut za standardizacijo. Razmnoževanje celote ali delov tega standarda ni dovoljeno.
EUROPEAN STANDARD EN 18235-2
NORME EUROPÉENNE
EUROPÄISCHE NORM
November 2026
ICS 35.030
Supersedes CWA 18245:2025
English version
Trusted data transactions - Part 2: Trustworthiness
requirements
Transactions de données de confiance - Partie 2: Vertrauenswürdige Datentransaktionen - Teil 2:
Exigences de crédibilité Anforderungen an die Vertrauenswürdigkeit
This European Standard was approved by CEN on 2 November 2026.
CEN and CENELEC members are bound to comply with the CEN/CENELEC Internal Regulations which stipulate the conditions for
giving this European Standard the status of a national standard without any alteration. Up-to-date lists and bibliographical
references concerning such national standards may be obtained on application to the CEN-CENELEC Management Centre or to
any CEN and CENELEC member.
This European Standard exists in three official versions (English, French, German). A version in any other language made by
translation under the responsibility of a CEN and CENELEC member into its own language and notified to the CEN-CENELEC
Management Centre has the same status as the official versions.
CEN and CENELEC members are the national standards bodies and national electrotechnical committees of Austria, Belgium,
Bulgaria, Croatia, Cyprus, Czech Republic, Denmark, Estonia, Finland, France, Germany, Greece, Hungary, Iceland, Ireland, Italy,
Latvia, Lithuania, Luxembourg, Malta, Netherlands, Norway, Poland, Portugal, Republic of North Macedonia, Romania, Serbia,
Slovakia, Slovenia, Spain, Sweden, Switzerland, Türkiye and United Kingdom.
CEN-CENELEC Management Centre:
Rue de la Science 23, B-1040 Brussels
© 2026 CEN/CENELEC All rights of exploitation in any form and by any means
Ref. No. EN 18235-2:2026 E
reserved worldwide for CEN national Members and for
CENELEC Members.
Contents Page
European foreword . 4
Introduction . 5
1 Scope . 6
2 Normative references . 6
3 Terms and definitions . 6
3.1 General. 6
3.2 Trust . 6
3.3 Data sharing . 7
4 Principles for trustworthiness requirements . 9
4.1 Introduction . 9
4.2 Phases of a data transaction . 9
4.3 Data rights . 9
4.4 Data product . 9
4.5 Data quality . 9
4.6 Data provenance and data lineage . 9
4.7 Observability and traceability of data transactions . 10
4.8 Data spaces . 10
4.9 Interoperability across data spaces . 10
4.10 Trust frameworks . 10
4.11 Trust policy dimensions . 11
4.12 Semantic data models . 11
5 Trustworthiness requirements . 11
5.1 Introduction . 11
5.2 General requirements . 11
5.2.1 Overview . 11
5.2.2 Identification of participants . 12
5.2.3 Policies, claims and evidence . 12
5.2.4 Operational and legal aspects of policies, claims and evidence. 13
5.2.5 Trust frameworks . 13
5.2.6 Data space rulebook . 14
5.3 Grant rights . 14
5.3.1 Overview . 14
5.3.2 Claims of granted data rights . 14
5.4 Publication . 15
5.4.1 Overview . 15
5.4.2 Verification of publication rights . 15
5.4.3 Catalogue metadata of the data product . 15
5.4.4 Data catalogue service requirements . 16
5.5 Discovery . 16
5.5.1 Overview . 16
5.5.2 Verification of rights and access control . 16
5.5.3 Discovery requirements . 16
5.5.4 Discovery recommended features . 17
5.6 Negotiation . 17
5.6.1 Overview . 17
5.6.2 Exchange of claims and evidence . 17
5.6.3 Recording of the data sharing contract . 17
5.7 Data exchange/ data sharing . 18
5.7.1 Overview . 18
5.7.2 Identification, authentication and authorization . 18
5.7.3 Observability of data transactions . 18
5.8 Data access and usage . 18
5.8.1 Overview . 18
5.8.2 Verification of access rights . 18
5.8.3 Usage of data. 19
Annex A (informative) Trust frameworks . 20
Annex ZA (informative) Relationship between this European Standard and the
interoperability requirements of Regulation (EU) 2023/2854 aimed to be covered
................................................................................................................................................................. 23
Bibliography . 25
European foreword
This document (EN 18235-2:2026) has been prepared by Technical Committee CEN/CLC JTC 25 “Data
Management, Dataspaces, Cloud and Edge”, the secretariat of which is held by UNI.
This European Standard shall be given the status of a national standard, either by publication of an
identical text or by endorsement, at the latest by May 2027, and conflicting national standards shall be
withdrawn at the latest by May 2027.
Attention is drawn to the possibility that some of the elements of this document may be the subject of
patent rights. CEN-CENELEC shall not be held responsible for identifying any or all such patent rights.
This document supersedes CWA 18245:2025.
This document has been prepared under a standardization request addressed to CEN and CENELEC by
the European Commission. The Standing Committee of the EFTA States subsequently approves these
requests for its Member States.
For the relationship with EU Legislation, see informative Annex ZA, which is an integral part of this
document.
Any feedback and questions on this document should be directed to the users’ national standards
body/national committee. A complete listing of these bodies can be found on the CEN and CENELEC
websites.
According to the CEN-CENELEC Internal Regulations, the national standards organisations of the
following countries are bound to implement this European Standard: Austria, Belgium, Bulgaria, Croatia,
Cyprus, Czech Republic, Denmark, Estonia, Finland, France, Germany, Greece, Hungary, Iceland, Ireland,
Italy, Latvia, Lithuania, Luxembourg, Malta, Netherlands, Norway, Poland, Portugal, Republic of North
Macedonia, Romania, Serbia, Slovakia, Slovenia, Spain, Sweden, Switzerland, Türkiye and the United
Kingdom.
Introduction
Sharing of data can have significant commercial, financial, privacy and other impacts on all stakeholders
involved. Therefore, it is important to identify the requirements for trustworthiness of data
transactions.
Data transactions can take place in many different organisational set-ups, requiring an interplay
between data rights holders, data providers, data users and any involved data intermediaries facilitating
the sharing of data, through technical, legal or other means.
Participants rely on commonly established technical and legal agreements, such as policies, semantic
models, protocols, and processes as well as trust frameworks for trusted data transactions. Participants
establish trust by exchanging claims and verifying evidence. A data space rulebook defines these
common specifications, agreements and trust framework which provides the common trust context for
data sharing within a data space. Participants establishing data sharing contracts use or refer to these
elements from a data space rulebook for trusted data sharing.
EN 18235-1:2026 (Trusted data transactions - Part 1) provides the terminology, concepts and
mechanisms for trusted data transactions. This document (Trusted data transactions - Part 2) defines
the trustworthiness requirements for trusted data transactions.
1 Scope
This document provides trustworthiness requirements and guidance for data space participants in
support of trusted data transactions.
Specifically, it defines a set of foundational principles for trusted data transactions, and establishes
general requirements and guidance that apply to all phases of a trusted data transaction, and specific
requirements for each phase of a trusted data transaction.
This document applies to all types of organizations participating in data spaces, regardless of their type
or size.
2 Normative references
The following documents are referred to in the text in such a way that some or all of their content
constitutes requirements of this document. For dated references, only the edition cited applies. For
undated references, the latest edition of the referenced document (including any amendments) applies.
EN 18235-1:2026, Trusted data transactions - Part 1: Terminology, concepts and mechanisms
3 Terms and definitions
For the purposes of this document, the terms and definitions given in EN 18235-1:2026 and the
following apply.
ISO and IEC maintain terminology databases for use in standardization at the following addresses:
— ISO Online browsing platform: available at https://www.iso.org/obp/
— IEC Electropedia: available at https://www.electropedia.org/
3.1 General
3.1.1
principle
fundamental truth, proposition or assumption that serves as foundation for a set of beliefs or behaviours
or for a chain of reasoning
[SOURCE: ISO 37000:2021, 3.2.1]
3.2 Trust
3.2.1
claim
statement of something to be true including associated conditions and limitations
Note 1 to entry: The statement of a claim does not mean that the only possible intent or desire is to show it is true.
Sometimes claims are made for the purpose of evaluating whether they are true or false or undertaking an effort
to establish what is true.
Note 2 to entry: In its entirety, a claim conforming to ISO/IEC/IEEE 15026-2 is an unambiguous declaration of an
assertion with any associated conditionality giving explicit details including limitations on values and uncertainty.
It could be about the future, present, or past.
EXAMPLE attributes of an entity such as its identity, statement of quality, conformity to standards, legal
status, location and so on
[SOURCE: ISO/IEC TR 15443-1:2012, 3.12, modified – added example]
3.2.2
evidence
information supporting a claim (3.2.1)
3.2.3
policy
set of rules related to a particular purpose
Note 1 to entry: A rule can be expressed as an obligation, an authorization, a permission or a prohibition.
Note 2 to entry: Policies enable the structured evaluation of claims (3.2.1).
Note 3 to entry: Policies can refer to simple identifiable objects or complex objects or types of objects to which
specified rules apply.
[SOURCE: ISO 19101-2:2018, modified – Notes added to entry]
3.2.4
reconciliation
process of evaluating and demonstrating that the claims (3.2.1) and evidence (3.2.2) satisfy the
requirements of the policy (3.2.3) in consideration
3.2.5
trustworthiness
quality or characteristic of something that is supported by verifiable evidence (3.2.2) which can be used
to establish trust
3.2.6
trust framework
set of requirements, rules, roles, responsibilities and assessment mechanisms in support of trust and
trustworthiness (3.2.5)
Note 1 to entry: it can include a trusted list of trust anchors and trust services and mechanisms to evaluate claims
(3.2.1) and evidence (3.2.2).
3.2.7
data integrity
property that data has not been altered or deleted by unauthorised parties
3.3 Data sharing
3.3.1
interoperability
ability of two or more systems or applications to exchange information and to mutually use the
information that has been exchanged
[SOURCE: ISO/IEC 22123-1:2023, 3.6.1]
3.3.2
data space governance framework
structured set of principles, processes, standards, protocols, rules and practices that guide and regulate
the governance, management and operations within a data space to ensure effective and responsible
leadership, control, and oversight
Note 1 to entry: It defines the functionalities supported in the data space and the associated data space roles,
including the data space governance authority and participants.
Note 2 to entry: ISO/IEC TR 38502:2017 defines governance framework as strategies, policies, decision-making
structures and accountabilities through which the organization’s governance arrangements operate.
Note 3 to entry: It can contain or refer to one or more trust frameworks (3.2.6).
[SOURCE: DSSC Data Spaces Blueprint v3.0, modified – Note 1 to entry added, Note 2 to entry added,
Note 3 to entry added]
3.3.3
data quality
degree to which a set of inherent characteristics of data fulfils requirements
[SOURCE: ISO 8000-2:2022, 3.8.1, modified – Note to entry removed]
3.3.4
observability
ability to monitor and verify the state and behaviour of a trusted data transaction
3.3.5
traceability
ability to log and track a trusted data transaction throughout its lifecycle
Note 1 to entry: Traceability enables compliance, accountability, dispute resolution, and proof of execution.
Note 2 to entry: Traceability ensures compliance with legal and ethical standards, allowing stakeholders to follow
the flow of data transactions while preserving trust and security.
3.3.6
data lineage
description of the entire history of data, including its creation, transformation, and the processes it
undergoes
Note 1 to entry: Data lineage provides a comprehensive map of how data evolves during its lifecycle.
3.3.7
data provenance
information on the place and time of origin, derivation or generation of data, proof of authenticity of the
data, or a record of past and present rights of the data
[SOURCE: ISO/IEC 5259-1:2024, 3.17, modified – “data set” replaced with “data”, “ownership” replaced
with “rights”]
3.3.8
semantic model
specification of the meaning of concepts, relationships, and constraints in a given domain, expressed
independently of data structures or data formats
3.3.9
data space rulebook
operational specifications derived from a data space governance framework (3.3.2)
Note 1 to entry: The data space rulebook is used to check compliance with a data space governance framework.
4 Principles for trustworthiness requirements
4.1 Introduction
The objective of this clause is to define the overarching principles that serve as foundation and in
support of the detailed requirements in Clause 5.
4.2 Phases of a data transaction
As identified in EN 18235-1, there are six activities (derived from three phases) of a data transaction:
1) grant rights,
2) publication,
3) discovery,
4) negotiation,
5) data exchange / data sharing,
6) data access and usage.
Trust is established during all activities of a trusted data transaction, involving all relevant participants,
each with defined roles specific to the activity.
4.3 Data rights
Data rights holders retain control over how their data are accessed and used through technical or legal
means.
NOTE 1 In the context of the personal data the data subject can be considered as data rights holders.
NOTE 2 Agreed data usage policies and relevant regulations can apply.
4.4 Data product
Data products are maintained throughout their lifecycle to ensure their suitability, quality and
accessibility.
Data rights holders and data providers rely on data governance processes and systems to manage their
data products (and data and metadata therein) along the lifecycle of the data product.
4.5 Data quality
Information on the quality of a data product is critical to ensuring trust in the transaction. The data
quality of a data product, when accurately described using metadata, enables to verify that the data are
suited to the purpose or application in which the data are intended to be used.
NOTE Regulations or data spaces can impose rules for the expected quality of certain types of data products.
4.6 Data provenance and data lineage
Where applicable, parties involved in trusted data transactions implement robust data governance
processes to ensure that metadata within the data product includes all necessary information on data
provenance and data lineage.
4.7 Observability and traceability of data transactions
Observability ensures that data transactions including the data access and usage are monitored and
diagnosed, providing insights into system behaviour, performance, security threats and potential
failures by continuously collecting and analysing relevant signals.
It ensures that data sharing systems are working correctly, in compliance with shared values, enhancing
confidence among stakeholders.
Traceability ensures that data transactions including the data access and usage are tracked, logged,
monitored, and verified throughout their lifecycle, providing an audit trail for accountability,
compliance, and dispute resolution.
Traceability provides transparency, helping participants and regulators ensure that data usage aligns
with policies, ethical guidelines, and contractual agreements.
NOTE Traceability can be applied to transactions within a data space as well as to transactions across
different data spaces.
4.8 Data spaces
Data spaces are environments where metadata, data and claims are being exchanged between
participants based on agreed rules and methods defined in a data space rulebook.
Being participants of the same data space, implying adherence to a common data space rulebook,
facilitates trusted data transactions.
NOTE Data spaces are not giant data warehouses or data lakes hosted in a shared, centralized storage.
4.9 Interoperability across data spaces
Since data spaces are sectoral or domain specific, parties are often participants in multiple data spaces.
EXAMPLE A manufacturer participates in manufacturing, logistics data space, energy data space, green deal
and sustainability data space, finance and insurance data space and more relevant data spaces.
Parties adhere to the rulebooks of the respective data spaces when sharing data across different sectors
or domains. Interoperable rulebooks facilitate connections between participants across different data
spaces.
NOTE Interoperability between data spaces can be implemented by establishing agreements and creating
explicit links between multiple rulebooks, which can be instantiated from an overarching rulebook.
4.10 Trust frameworks
Trust frameworks provide a way to establish trust between participants in a data transaction.
A data space relies on one or more trust frameworks.
A data space can combine and/or extend trust frameworks to fit their needs, or alternatively define its
own trust framework, as long as the result complies with the requirements for trust frameworks in
Clause 5.
The use of interoperable trust frameworks helps creating synergy effects across different sectors or
domains, enabling connections across data spaces and other data ecosystems.
Further information on trust frameworks can be found in Annex A.
4.11 Trust policy dimensions
Trusted data transactions span across use cases, business models, IT architectures while adhering to
laws and regulations across multiple jurisdictions.
Trust policies for data transactions address three dimensions: Legal, operational and technical. While
these three dimensions are interdependent, functional separation of policies along these three
dimensions helps to enable reuse and interoperability in different contexts.
EXAMPLE Policies in trusted data transactions can define data space participation policies (operational),
access to offers (technical), data contract policies (legal) or data usage policies (legal).
4.12 Semantic data models
For trusted exchange of data, it is assumed that all participants have a clear, meaningful and
unambiguous understanding of the process.
Semantic data models provide participants with the information to interpret the various types of data
and metadata involved in the operation of a data space and data transactions in a meaningful and
uniform manner.
Such semantic data models describe both the meaning of the data that is being exchanged and the
metadata that is used to facilitate the exchange of the data.
5 Trustworthiness requirements
5.1 Introduction
The primary objective of this clause is to define a comprehensive set of trustworthiness requirements
for trusted data transactions, taking the principles discussed in Clause 4 as a basis.
To this end, the clause is structured around the six activities (clustered in three phases) of a data
transaction identified in EN 18235-1:
1) grant rights,
2) publication,
3) discovery,
4) negotiation,
5) data exchange / data sharing, and
6) data access and usage.
5.2 General requirements
5.2.1 Overview
This clause covers general trustworthiness requirements that apply to all phases of a trusted data
transaction, addressing the role of trust frameworks and data space governance authorities.
SIST EN 18235-2:202
...